KUBERNETES (K8s) – DEFINITIONS AND ACRONYMS
Plain-text reference guide for Kubernetes administrators and CKA preparation.
- KUBERNETES FUNDAMENTALS
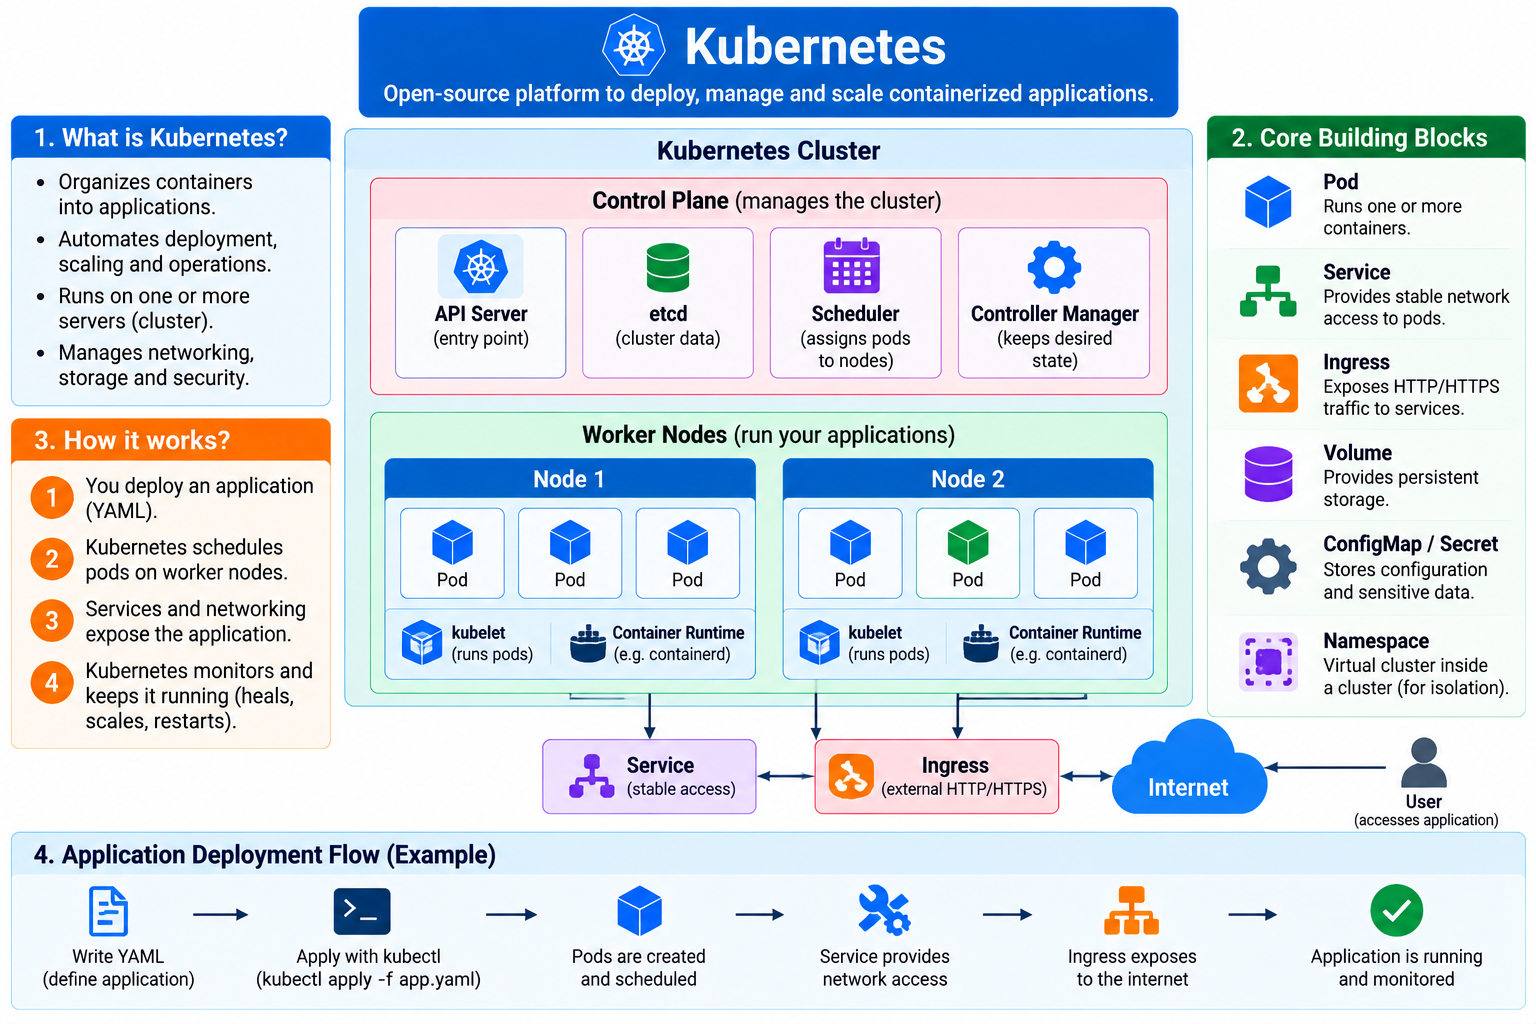
K8s – Kubernetes (K + 8 letters + s).
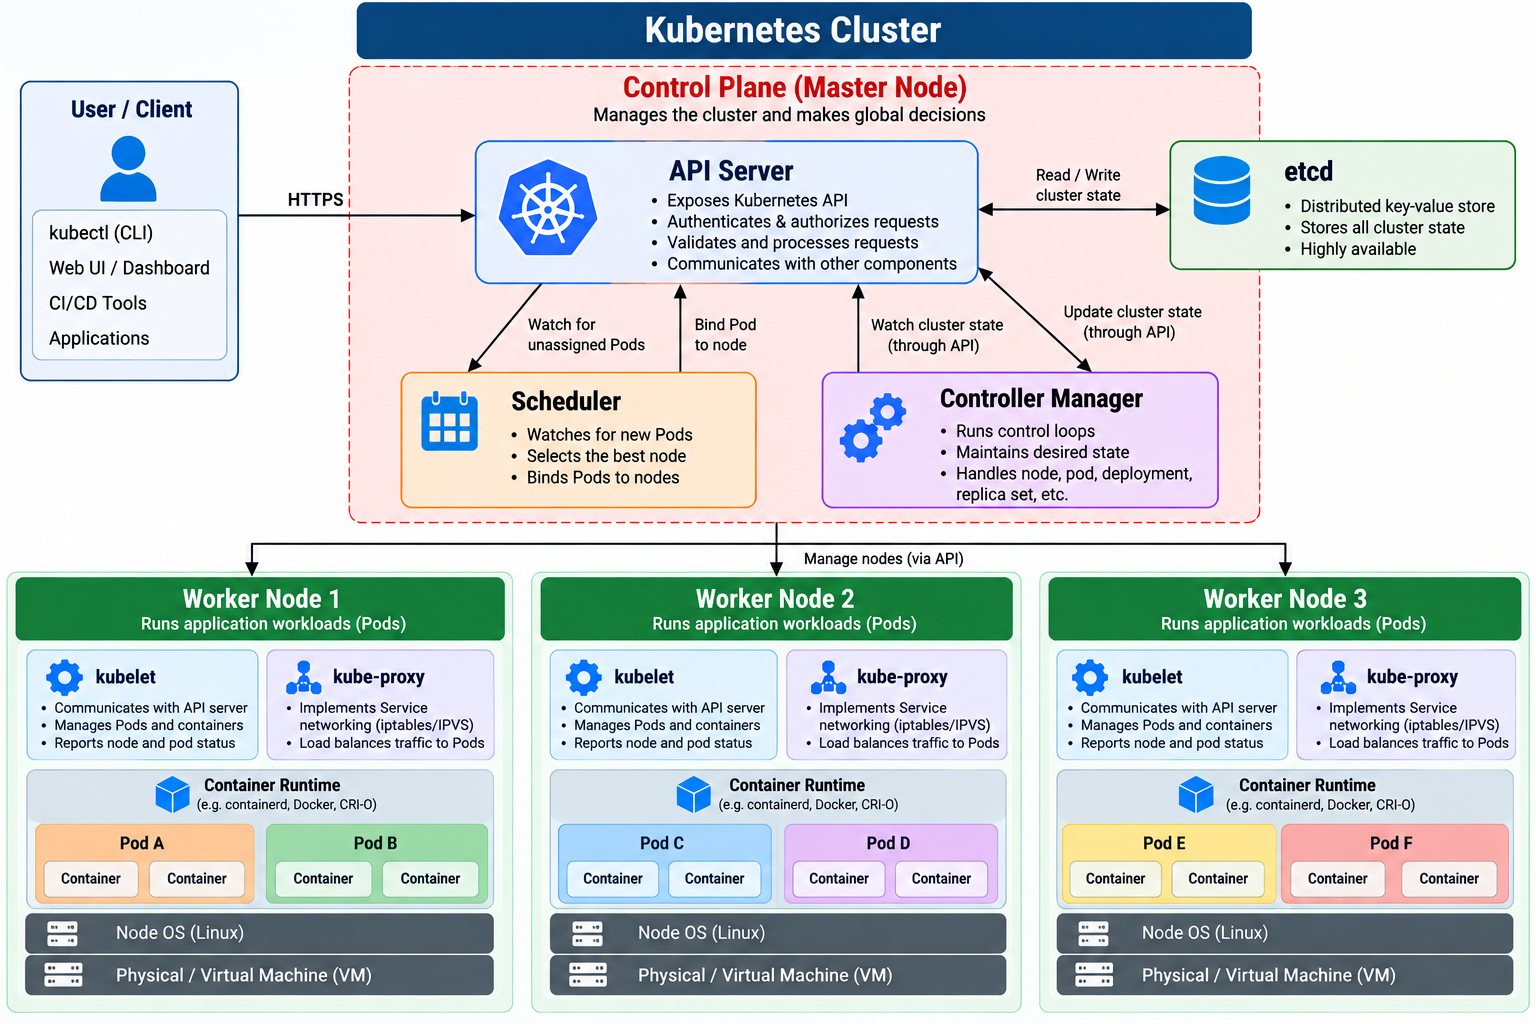
Cluster – Group of nodes managed by Kubernetes.
Node – Physical or virtual machine participating in a cluster.
Control Plane – Components responsible for managing cluster state.
Worker Node – Machine that runs application workloads.
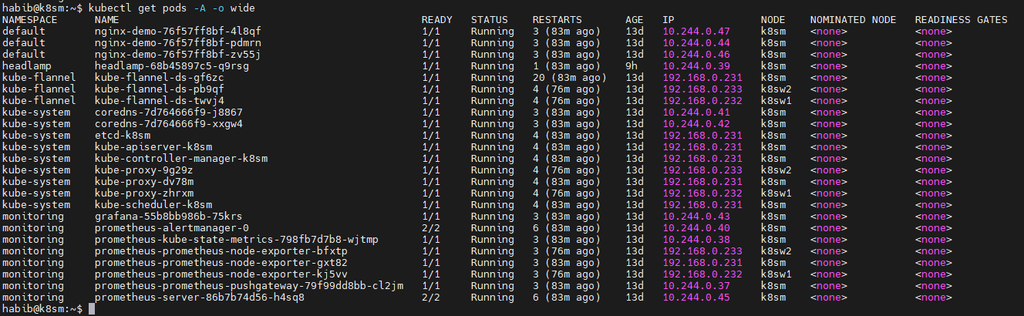
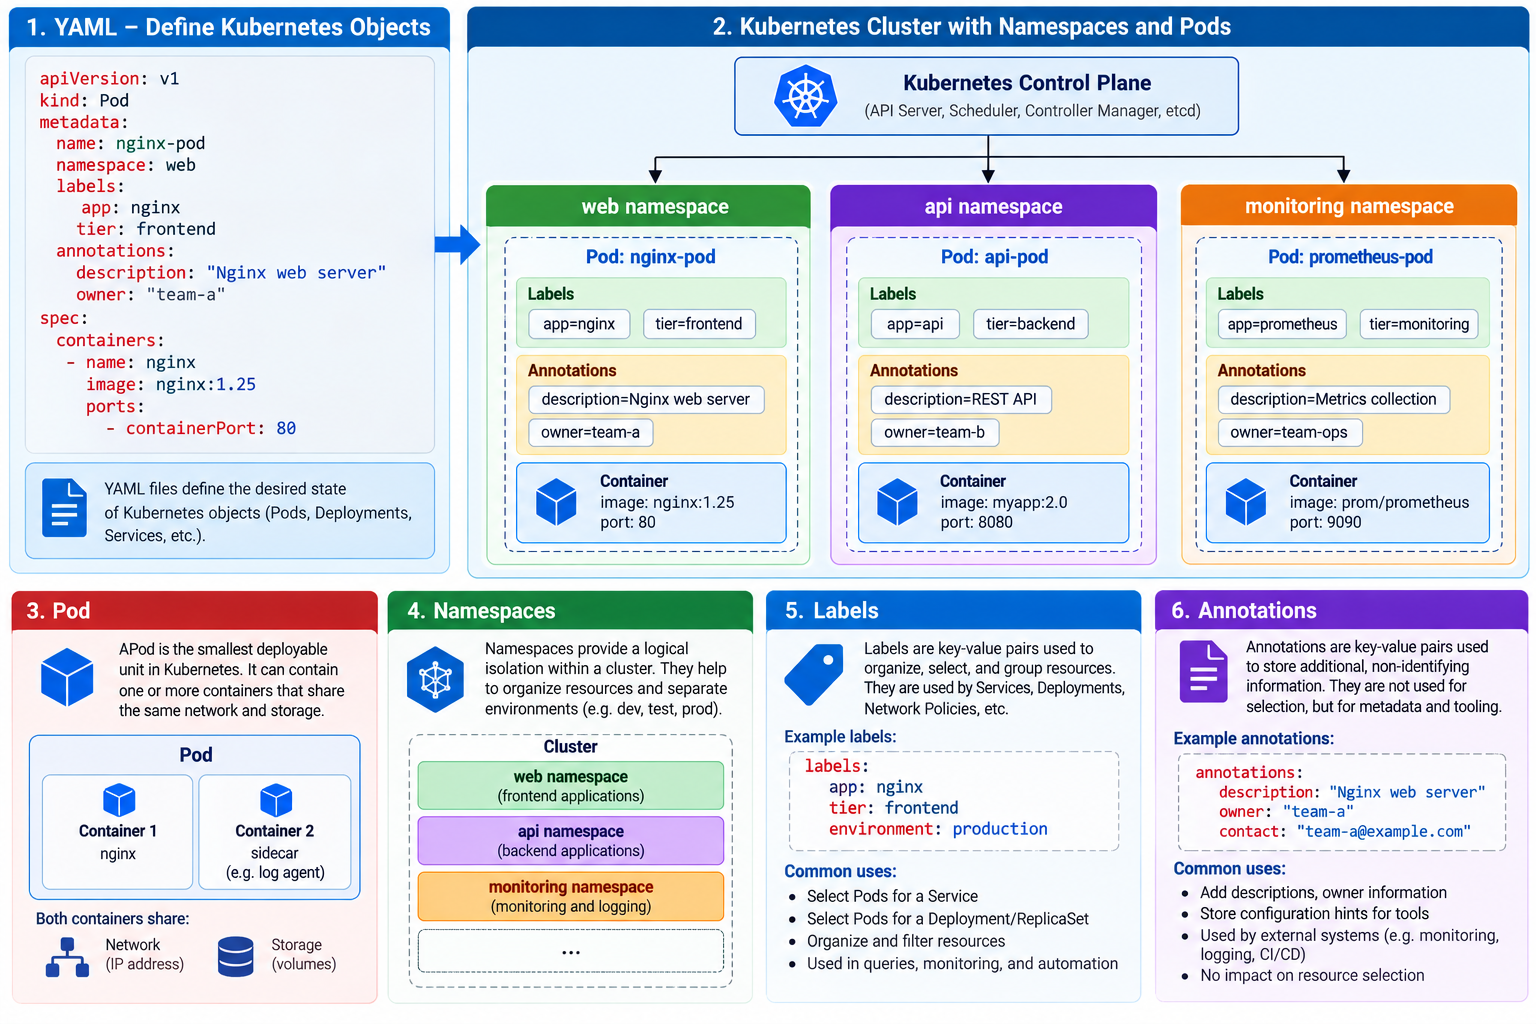
Pod – Smallest deployable Kubernetes unit; one or more containers.
Container – Isolated application process environment.
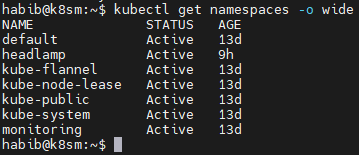
Namespace – A Namespace is a Kubernetes resource that logically separates and organizes resources within a single cluster.
It provides:
- Resource Isolation: Separates applications and workloads logically.
- Resource Management: Controls CPU, memory, and other resource quotas.
- Access Control: Supports namespace-specific RBAC permissions.
- Organization: Groups resources by team, project, or environment.
- Name Separation: Allows resources with the same name in different namespaces.
Use Cases: Development, testing, production, and multi-team environments.
Key Point: Namespaces provide logical separation, not complete security or network isolation by default.
Manifest – YAML or JSON definition of a Kubernetes resource.
Desired State – Target configuration Kubernetes attempts to maintain.
Reconciliation – Process of bringing actual state toward desired state.
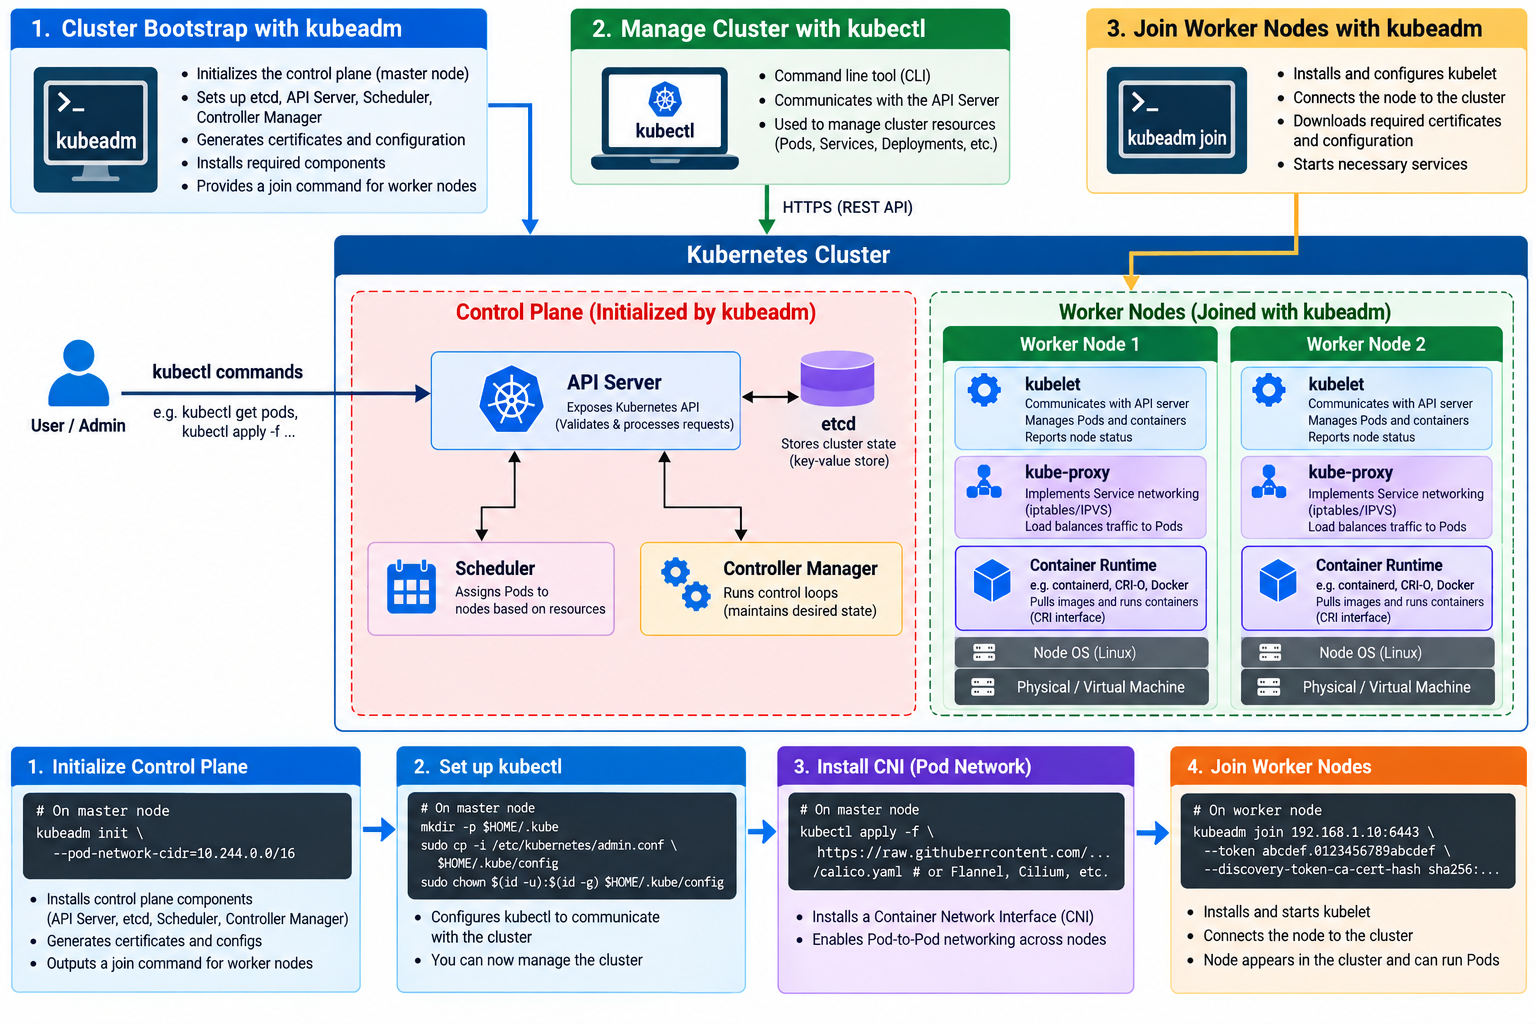
kubectl – Command-line client for the Kubernetes API.
kubeconfig – Configuration for clusters, users, and contexts.
Context – Selected cluster, user, and optional namespace.
API – Application Programming Interface.
YAML – YAML Ain’t Markup Language.
JSON – JavaScript Object Notation.
CRI – Container Runtime Interface.
OCI – Open Container Initiative.
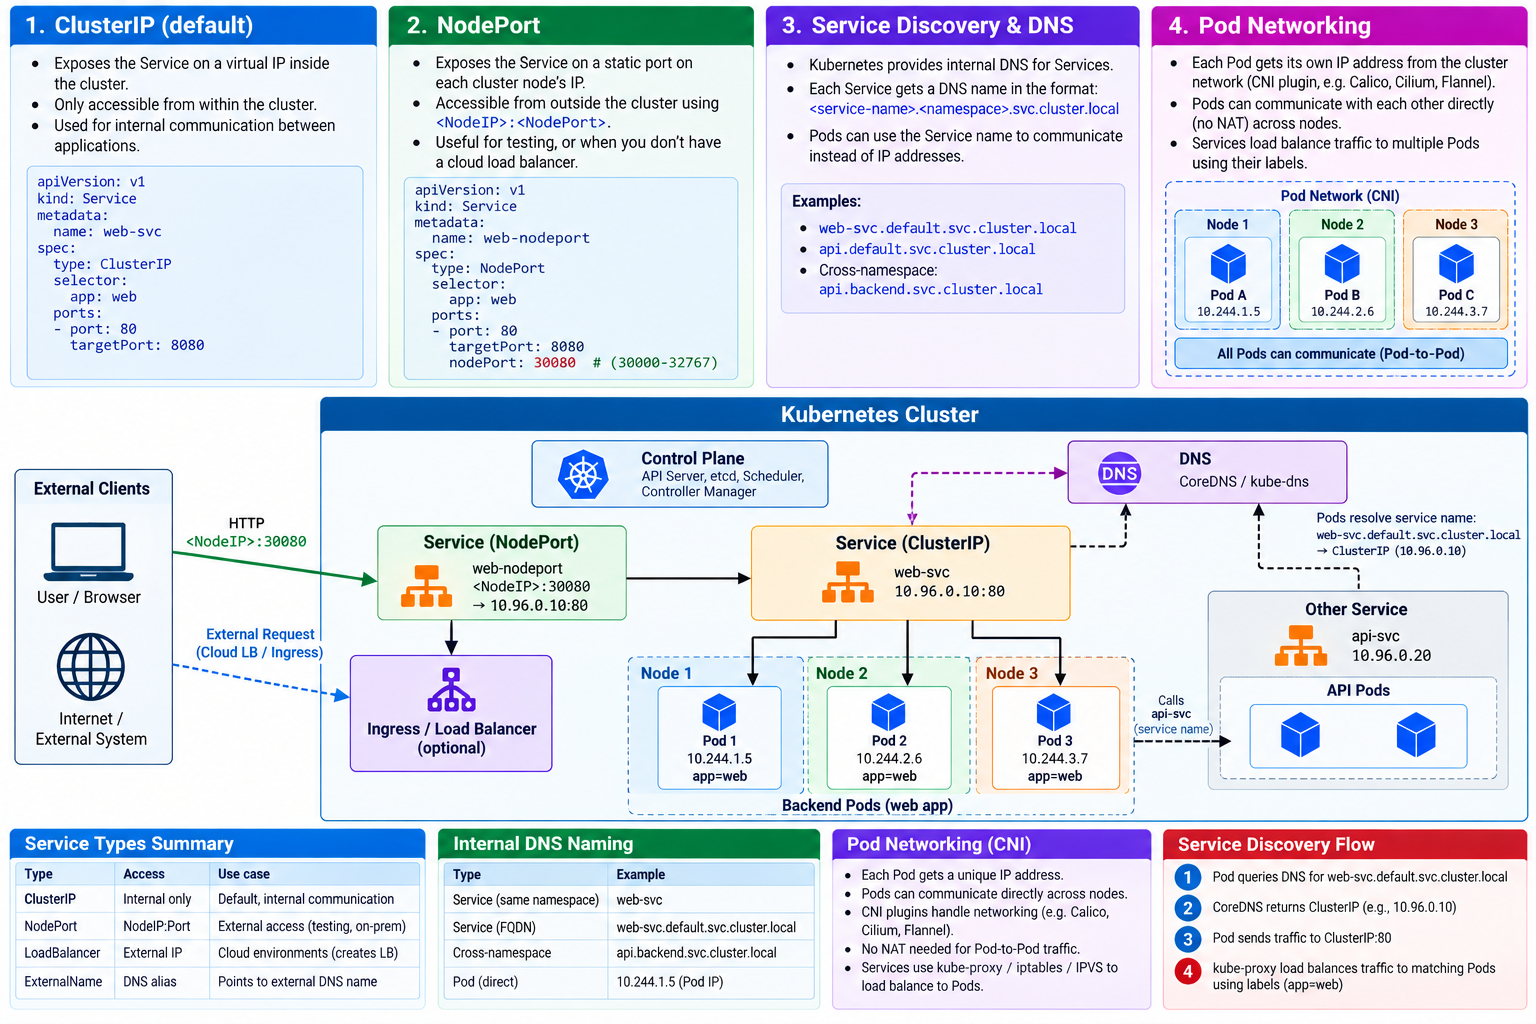
CNI – Container Network Interface.
CSI – Container Storage Interface.
- CONTROL PLANE AND NODE COMPONENTS
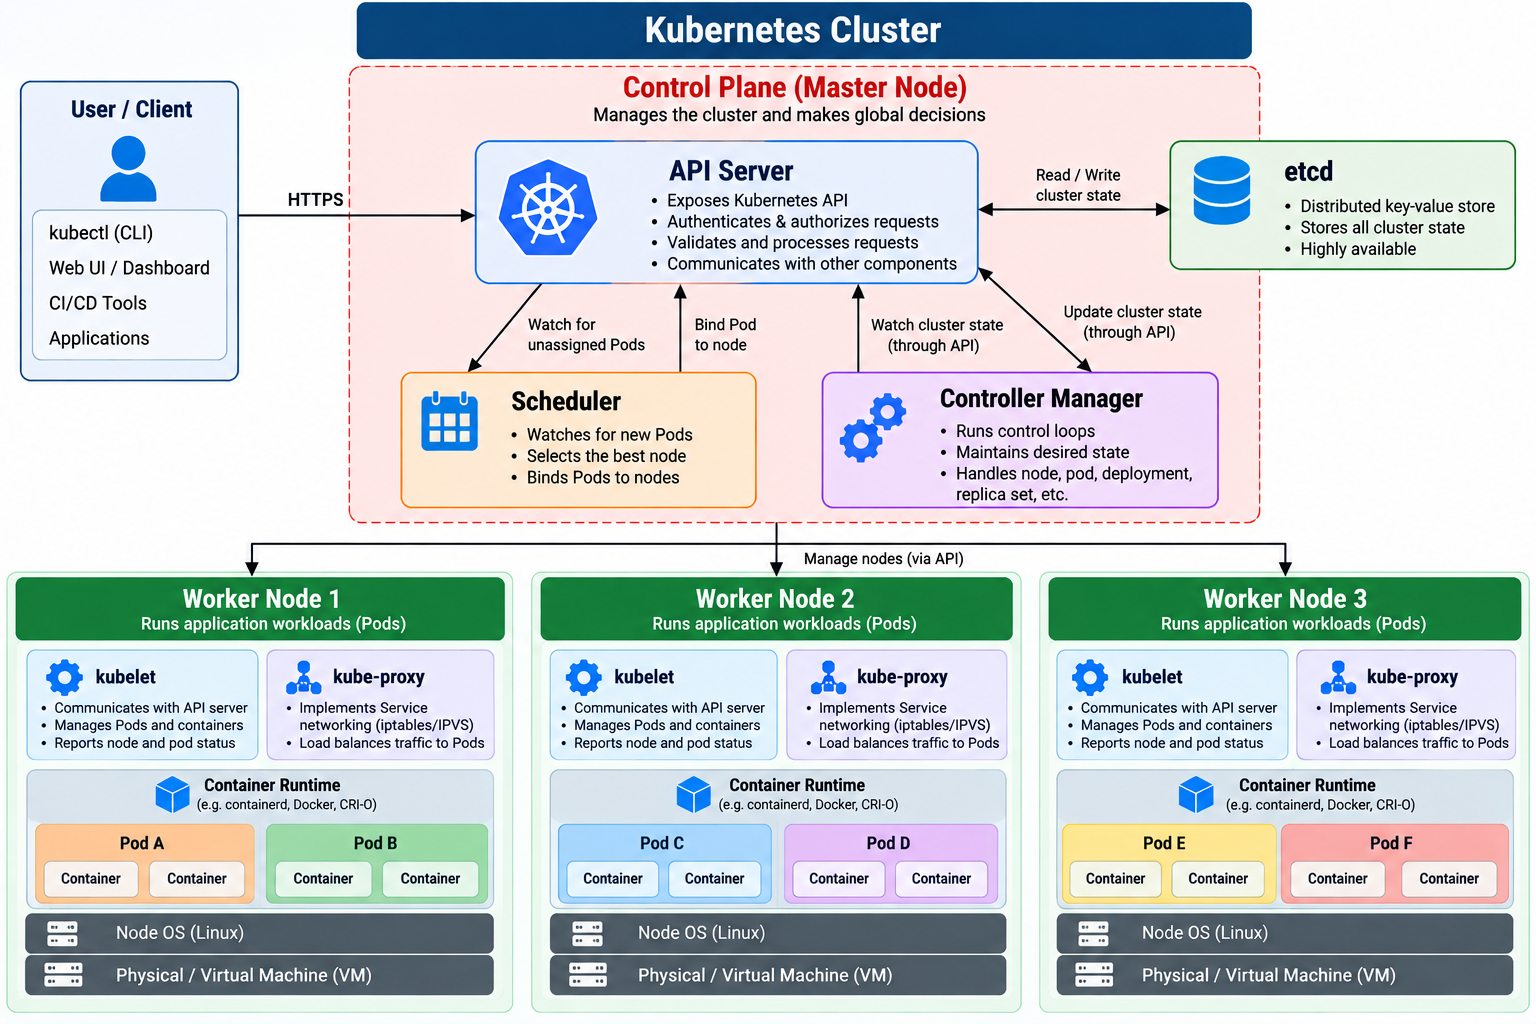
kube-apiserver – Exposes and validates the Kubernetes API.
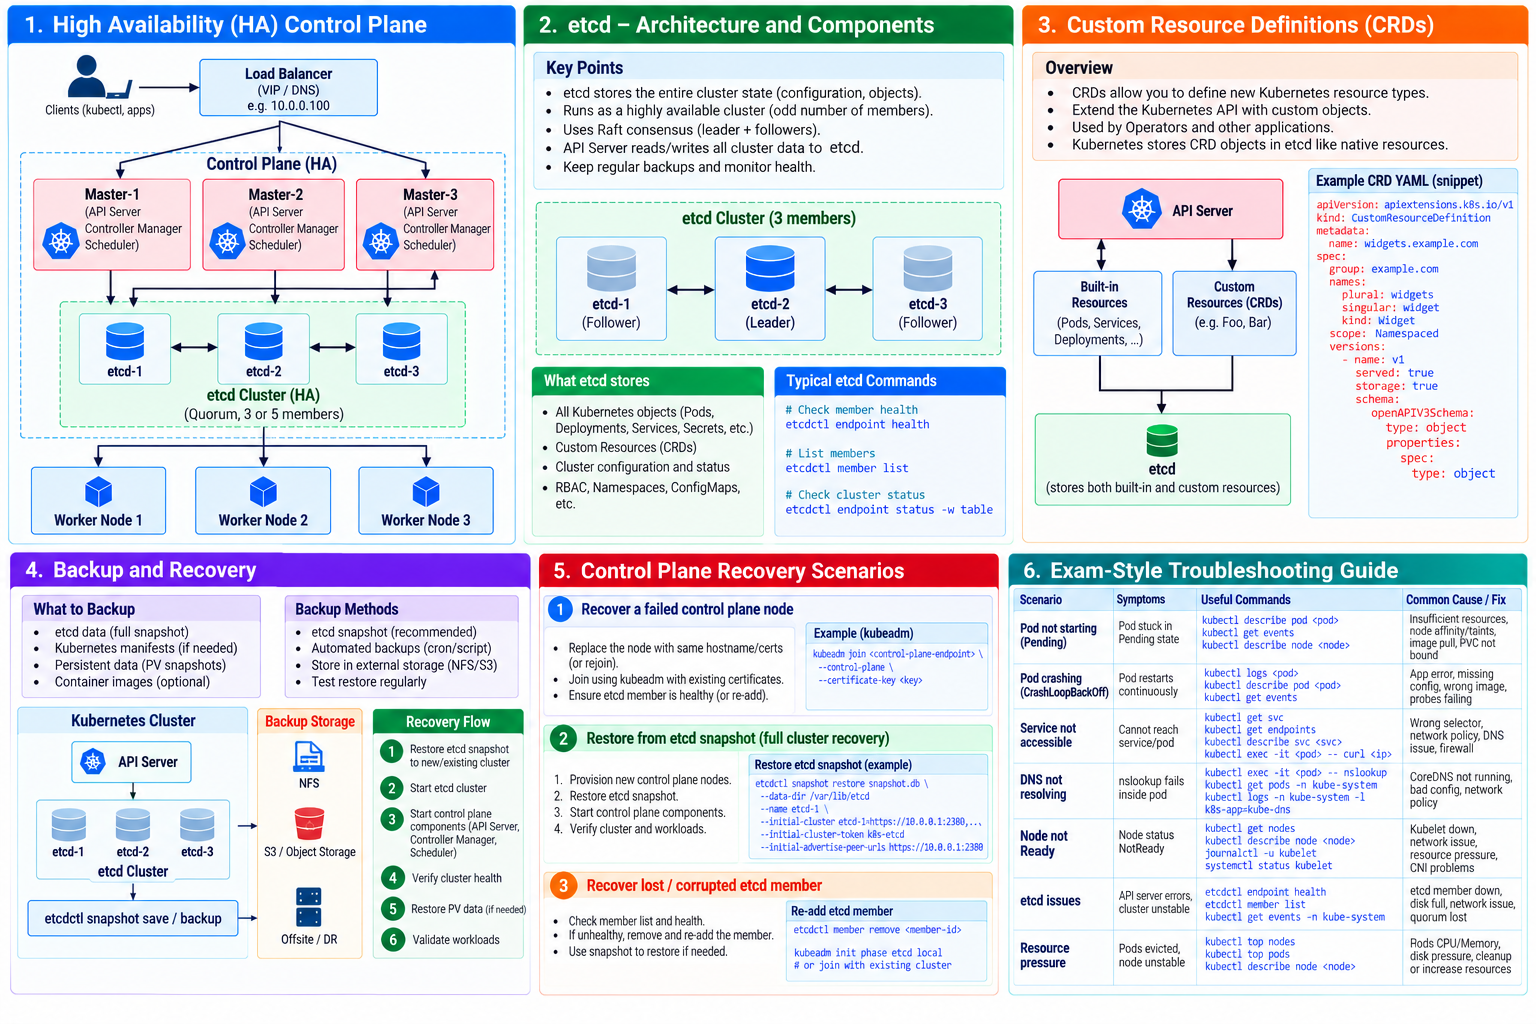
etcd – Distributed key-value database storing cluster state.
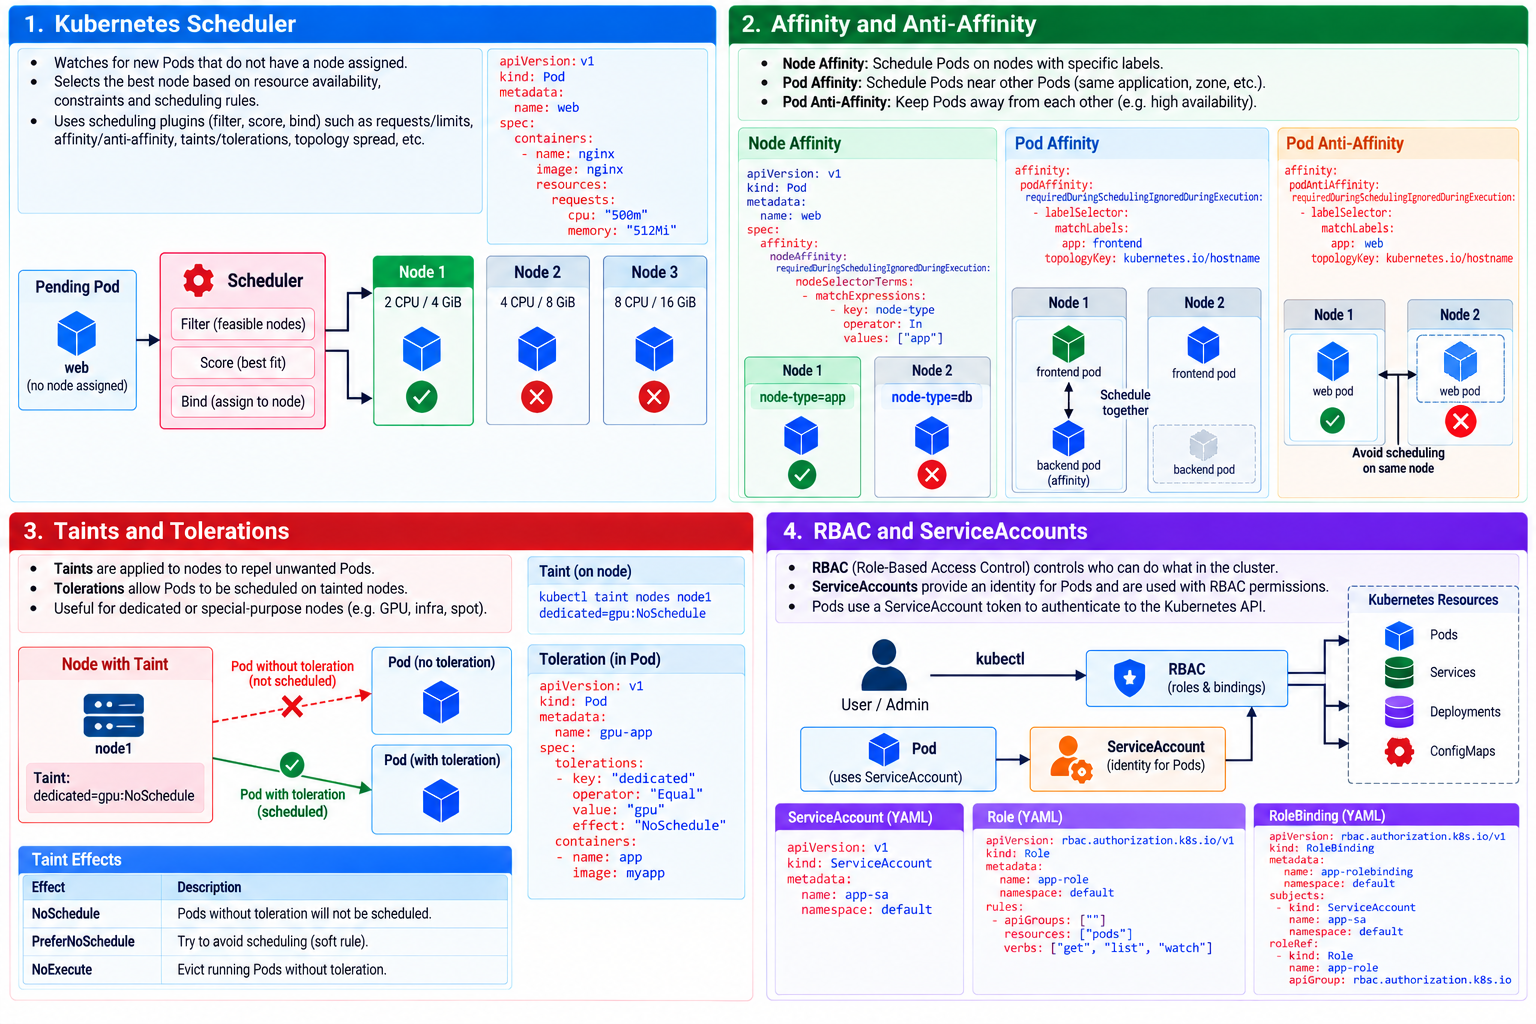
kube-scheduler – Assigns unscheduled Pods to suitable nodes.
kube-controller-manager – Runs core reconciliation controllers.
cloud-controller-manager (CCM) – Integrates cloud provider infrastructure.
kubelet – Node agent that manages Pod execution.
kube-proxy – Implements Service networking on nodes (when deployed).
CRD – CustomResourceDefinition; adds a custom API resource type.
Leader Election – Selects an active leader among controller replicas.
- WORKLOADS AND CONTROLLERS
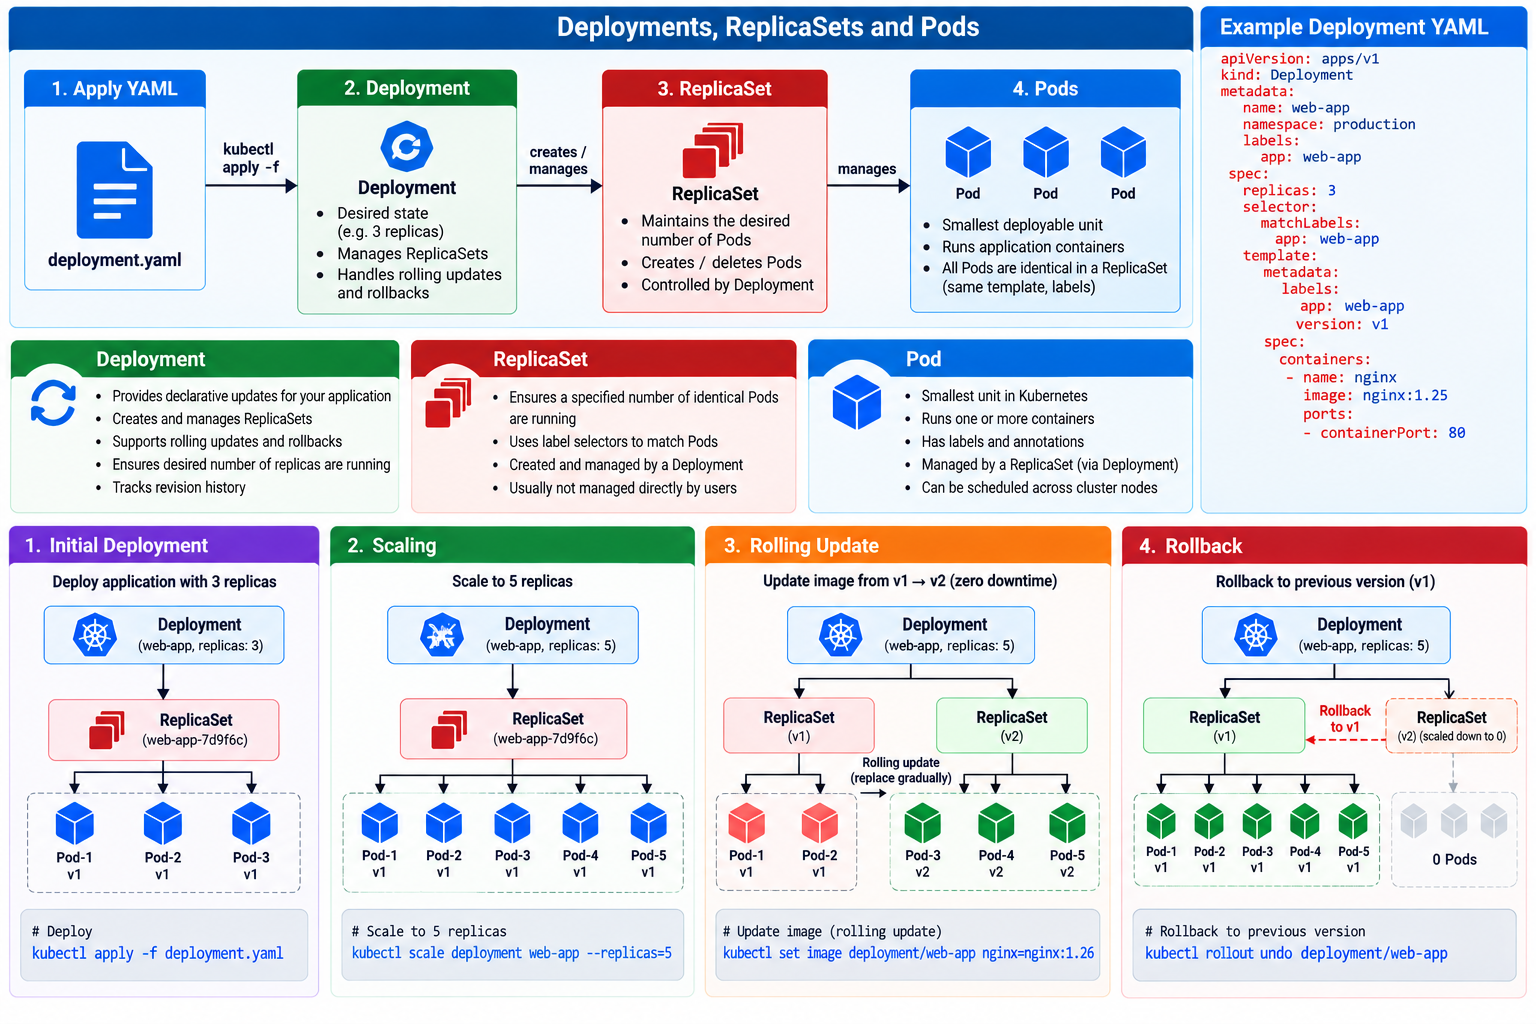
Deployment – A Deployment is a Kubernetes resource that manages application Pods through ReplicaSets.
It provides:
- Scaling: Increase or decrease Pod replicas.
- Self-Healing: Automatically replace failed Pods.
- Rolling Updates: Update applications with minimal downtime.
- Rollback: Restore previous application versions.
- Desired State: Maintain the specified number of replicas.
Architecture: Deployment → ReplicaSet → Pods
ReplicaSet – A ReplicaSet is a Kubernetes resource that ensures the desired number of identical Pod replicas are running at all times.
It provides:
- Pod Management: Creates and maintains Pods.
- Self-Healing: Replaces failed or deleted Pods.
- Scaling: Maintains the specified number of replicas.
- High Availability: Helps keep applications running through multiple Pod replicas.
Architecture: Deployment → ReplicaSet → Pods
Key Point: ReplicaSets are typically managed by Deployments rather than directly.
StatefulSet – A StatefulSet is a Kubernetes resource that manages stateful applications requiring stable identities, persistent storage, and ordered deployment.
It provides:
- Stable Identity: Each Pod gets a unique, persistent name.
- Persistent Storage: Maintains dedicated storage for each Pod.
- Ordered Deployment: Creates and removes Pods in a defined order.
- Self-Healing: Replaces failed Pods while preserving their identity.
- Stable Networking: Provides predictable Pod DNS identities.
Architecture: StatefulSet → Pods → Persistent Volumes (PVCs)
Use Cases: Databases (MySQL, PostgreSQL, MongoDB), Kafka, and other stateful applications.
Key Point: Unlike Deployments, StatefulSets maintain stable Pod identities and storage across Pod replacements.
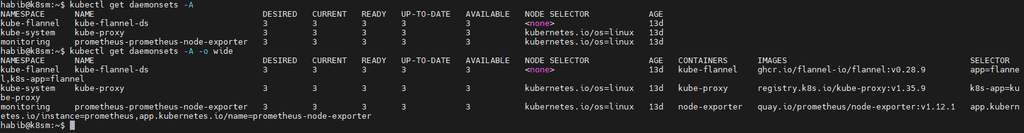
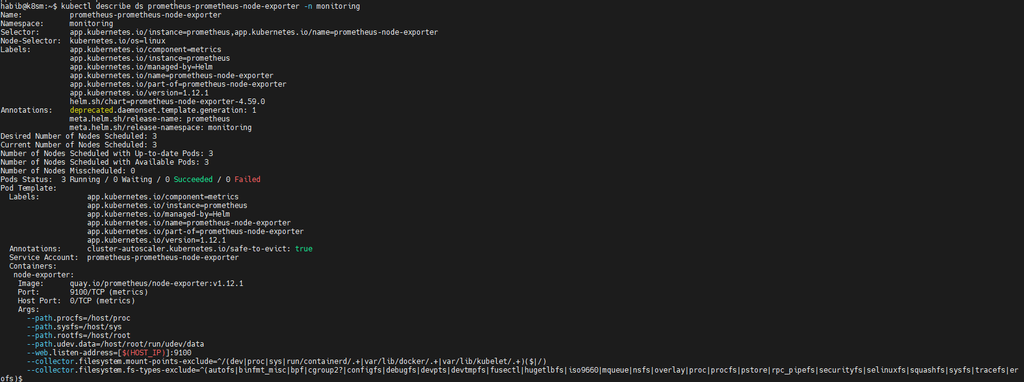
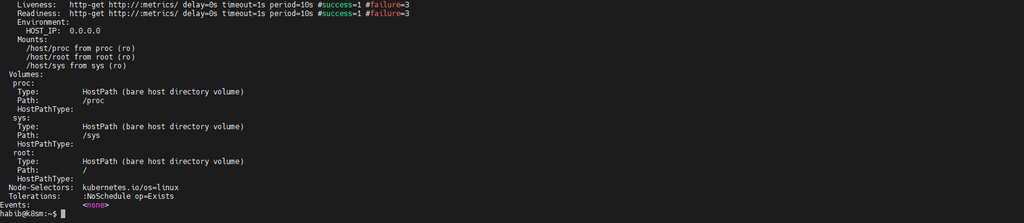
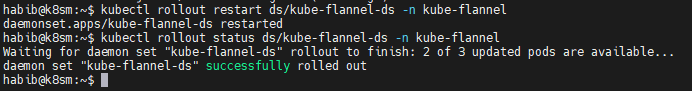
DaemonSet -A DaemonSet is a Kubernetes resource that ensures a copy of a specific Pod runs on every eligible node (or selected nodes) in a cluster.
It provides:
- Node-Level Deployment: Runs one Pod per eligible node.
- Automatic Scheduling: Deploys Pods when new eligible nodes join.
- Self-Healing: Replaces failed or deleted Pods.
- Centralized Management: Manages node-level services across the cluster.
Architecture: DaemonSet → One Pod per Eligible Node
Use Cases: Log collection (Fluent Bit), monitoring (Prometheus Node Exporter), and networking (Flannel, Calico).
Key Point: Unlike Deployments, DaemonSets ensure node-level Pod coverage rather than maintaining a fixed number of replicas.
Job – Runs tasks to completion.
CronJob (CJ) – Creates Jobs on a schedule.
Init – Container Runs setup tasks before application containers start.
Sidecar – Container Helper container supporting an application container.
Ephemeral Container – Temporary container for interactive troubleshooting.
HPA – Horizontal Pod Autoscaler; adjusts replica count.
VPA – Vertical Pod Autoscaler; recommends/adjusts Pod resources.
PDB – Pod Disruption Budget; limits voluntary disruptions.
Rolling Update – Gradually replaces old Pods with new Pods.
Rollback – Returns a workload to an earlier revision.
Restart Policy – Rules governing container restarts within a Pod.
- NETWORKING AND SERVICE DISCOVERY
CNI – Container Network Interface.
CoreDNS – DNS server commonly used for Kubernetes discovery.
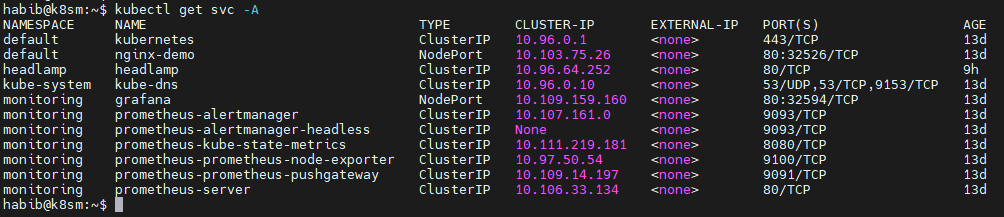
ClusterIP – Service type reachable within the cluster.
NodePort – A NodePort is a Kubernetes Service type that exposes an application externally through a specific port on every cluster node.
It provides:
- External Access: Allows access using
NodeIP:NodePort. - Port Allocation: Uses ports 30000–32767 by default.
- Traffic Distribution: Routes incoming traffic to backend Pods.
- Node-Level Access: Makes the Service accessible through any reachable node IP.
Architecture: Client → NodeIP:NodePort → Kubernetes Service → Pods
Example Command:
LoadBalancer – A LoadBalancer is a Kubernetes Service type that exposes an application externally and distributes incoming network traffic across its backend Pods.
It provides:
- External Access: Exposes applications through an external IP address.
- Traffic Distribution: Routes incoming traffic to available backend Pods.
- High Availability: Distributes traffic across multiple Pod replicas.
- Cloud Integration: Uses cloud provider load balancers or solutions like MetalLB.
Architecture: Client → External Load Balancer → Kubernetes Service → Pods
Example Command:
kubectl expose deployment nginx \
  --type=LoadBalancer \
  --port=80
Key Point: A LoadBalancer Service provides external access to applications. On bare-metal clusters, an additional load balancer implementation, such as MetalLB, is typically required.
ExternalName – Service type returning a DNS alias.
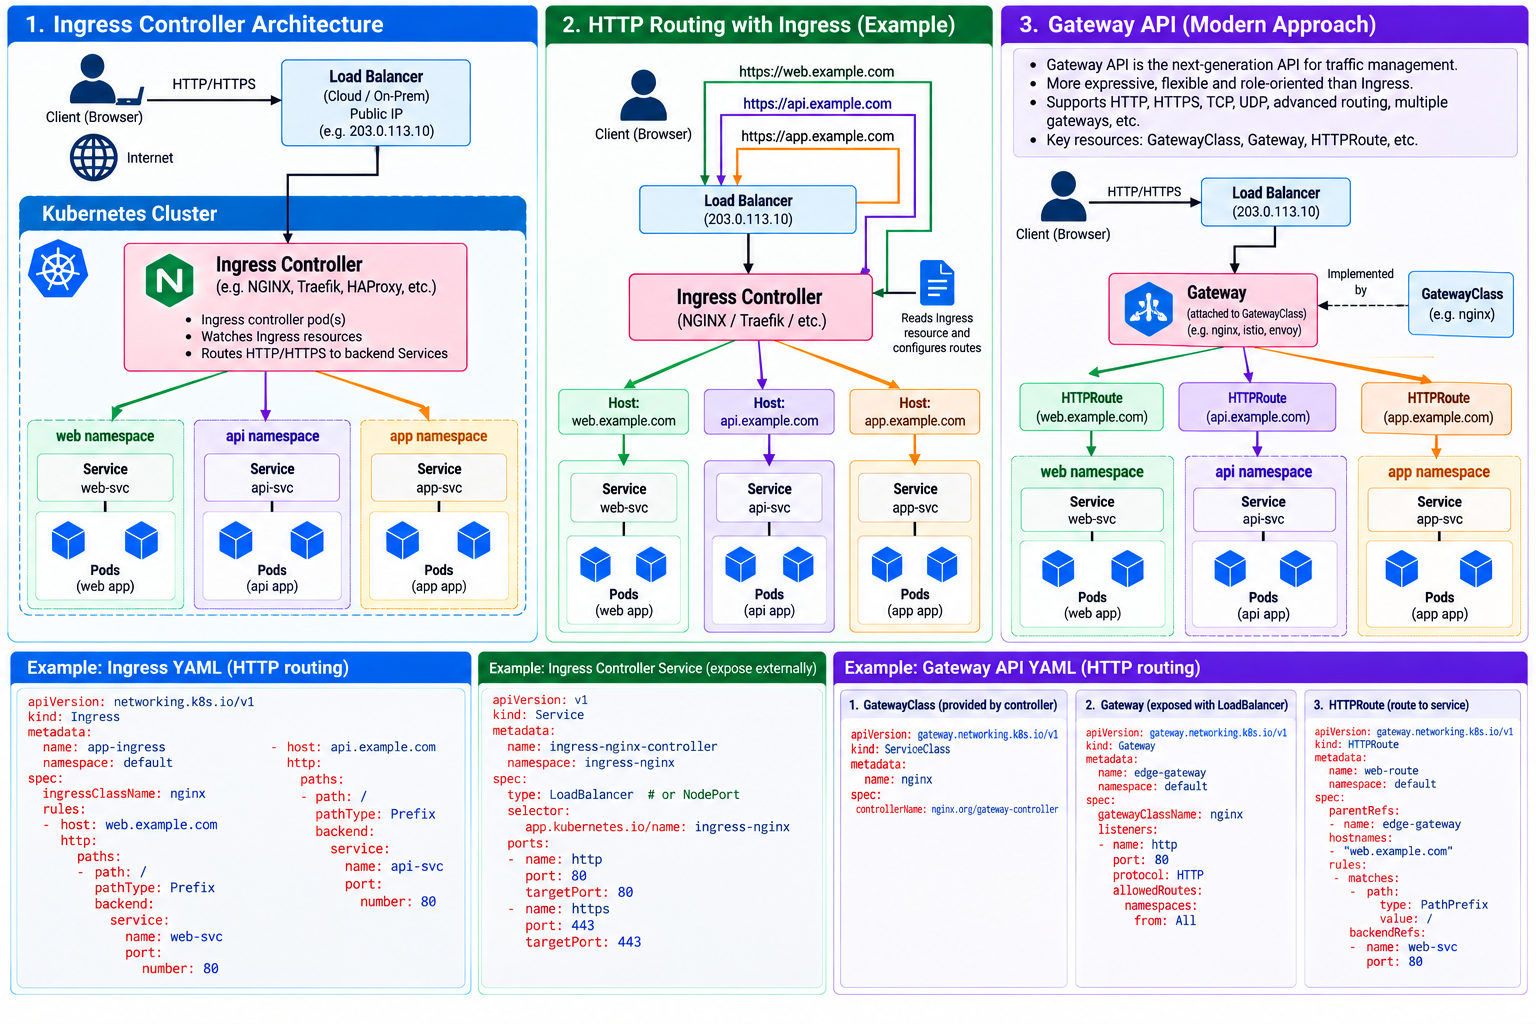
Ingress API – resource describing HTTP/HTTPS routing rules.
Ingress – Controller Software that implements Ingress rules.
Gateway API – APIs for flexible service traffic routing.
NetworkPolicy – Policy controlling selected Pod ingress/egress traffic.
Pod CIDR – IP address range used for Pods.
Service CIDR – IP address range used for Services.
eBPF – Extended Berkeley Packet Filter.
Flannel – Kubernetes CNI network plugin.
Calico – Kubernetes networking and network policy solution.
Cilium – eBPF-based networking, security, and observability solution.
- STORAGE
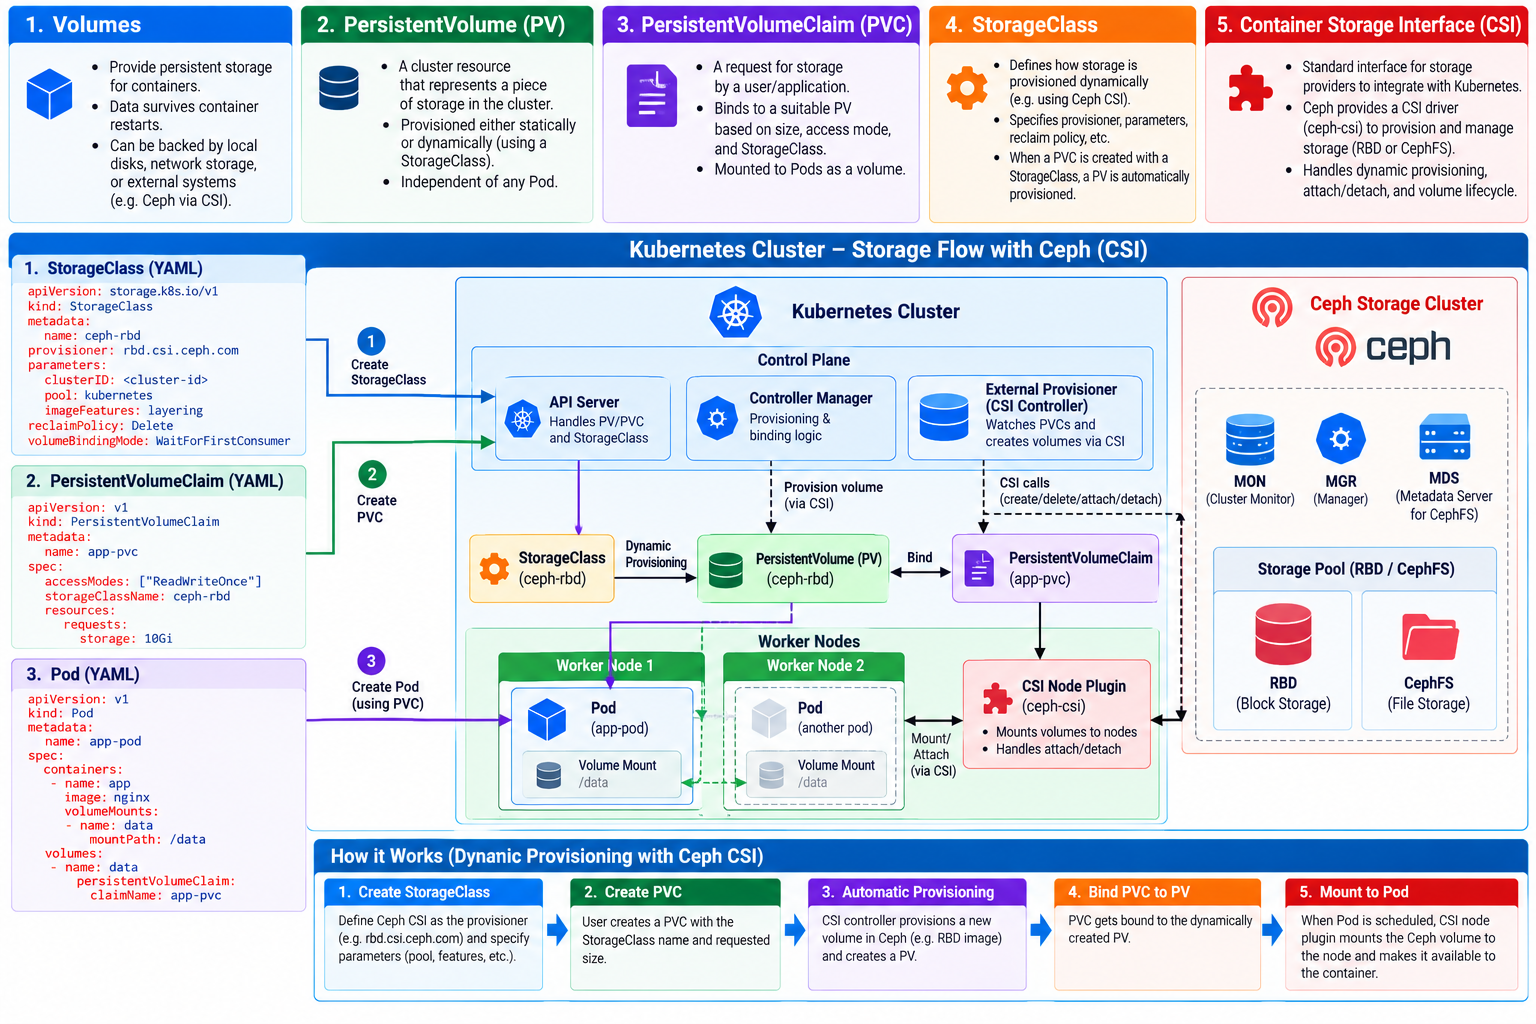
Volume – Storage exposed to containers in a Pod.
PV – PersistentVolume; cluster storage resource.
PVC – PersistentVolumeClaim; request for persistent storage.
SC – StorageClass; defines storage provisioning properties.
CSI – Container Storage Interface.
Storage Provisioner – Component that provisions storage volumes.
Dynamic Provisioning – Automatic creation of PVs for claims.
Static Provisioning – Pre-created PVs managed by administrators.
emptyDir – Ephemeral volume tied to a Pod’s lifetime.
hostPath – Mount of a node filesystem path into a Pod.
RWO – ReadWriteOnce; read/write mount by one node.
ROX – ReadOnlyMany; read-only mounts by many nodes.
RWX – ReadWriteMany; read/write mounts by many nodes.
RWOP – ReadWriteOncePod; exclusive read/write use by one Pod.
NFS – Network File System.
iSCSI – Internet Small Computer Systems Interface.
VolumeSnapshot – Snapshot resource supported by CSI snapshot components.
- SECURITY AND ACCESS CONTROL
RBAC – Role-Based Access Control.
SA – ServiceAccount; identity for workloads.
Role – Set of permissions within a namespace.
ClusterRole – Permissions that can apply cluster-wide or to namespaces.
RoleBinding – Grants Role or ClusterRole permissions in a namespace.
ClusterRoleBinding – Grants ClusterRole permissions cluster-wide.
TLS – Transport Layer Security.
mTLS – Mutual Transport Layer Security.
CA – Certificate Authority.
CSR – Certificate Signing Request.
OIDC – OpenID Connect.
JWT – JSON Web Token.
PSA – Pod Security Admission.
PSS – Pod Security Standards.
SCC – Security Context Constraints (OpenShift).
Secret – Resource storing sensitive configuration data.
ConfigMap (CM) – Resource storing non-confidential configuration data.
Admission Controller – Validates or mutates API requests.
SecurityContext -Pod/container security settings.
- SCHEDULING AND RESOURCE MANAGEMENT
CPU Request – CPU quantity used by the scheduler for placement.
CPU Limit Upper – CPU usage bound for a container.
Memory Request – Memory quantity used for scheduling.
Memory Limit – Upper memory bound for a container.
QoS – Quality of Service classification for Pods.
Guaranteed QoS – when CPU/memory requests equal limits for all containers.
Burstable QoS – with some requests/limits but not Guaranteed.
BestEffort QoS – without CPU/memory requests or limits.
Taint – Node restriction that repels non-tolerating Pods.
Toleration – Pod setting allowing scheduling past a matching taint.
NodeSelector – Label-based node selection.
Node Affinity – Flexible node scheduling constraints/preferences.
Pod Affinity – Places Pods near matching Pods.
Pod Anti-Affinity – Separates Pods from matching Pods.
Eviction – Removal of a Pod from a node.
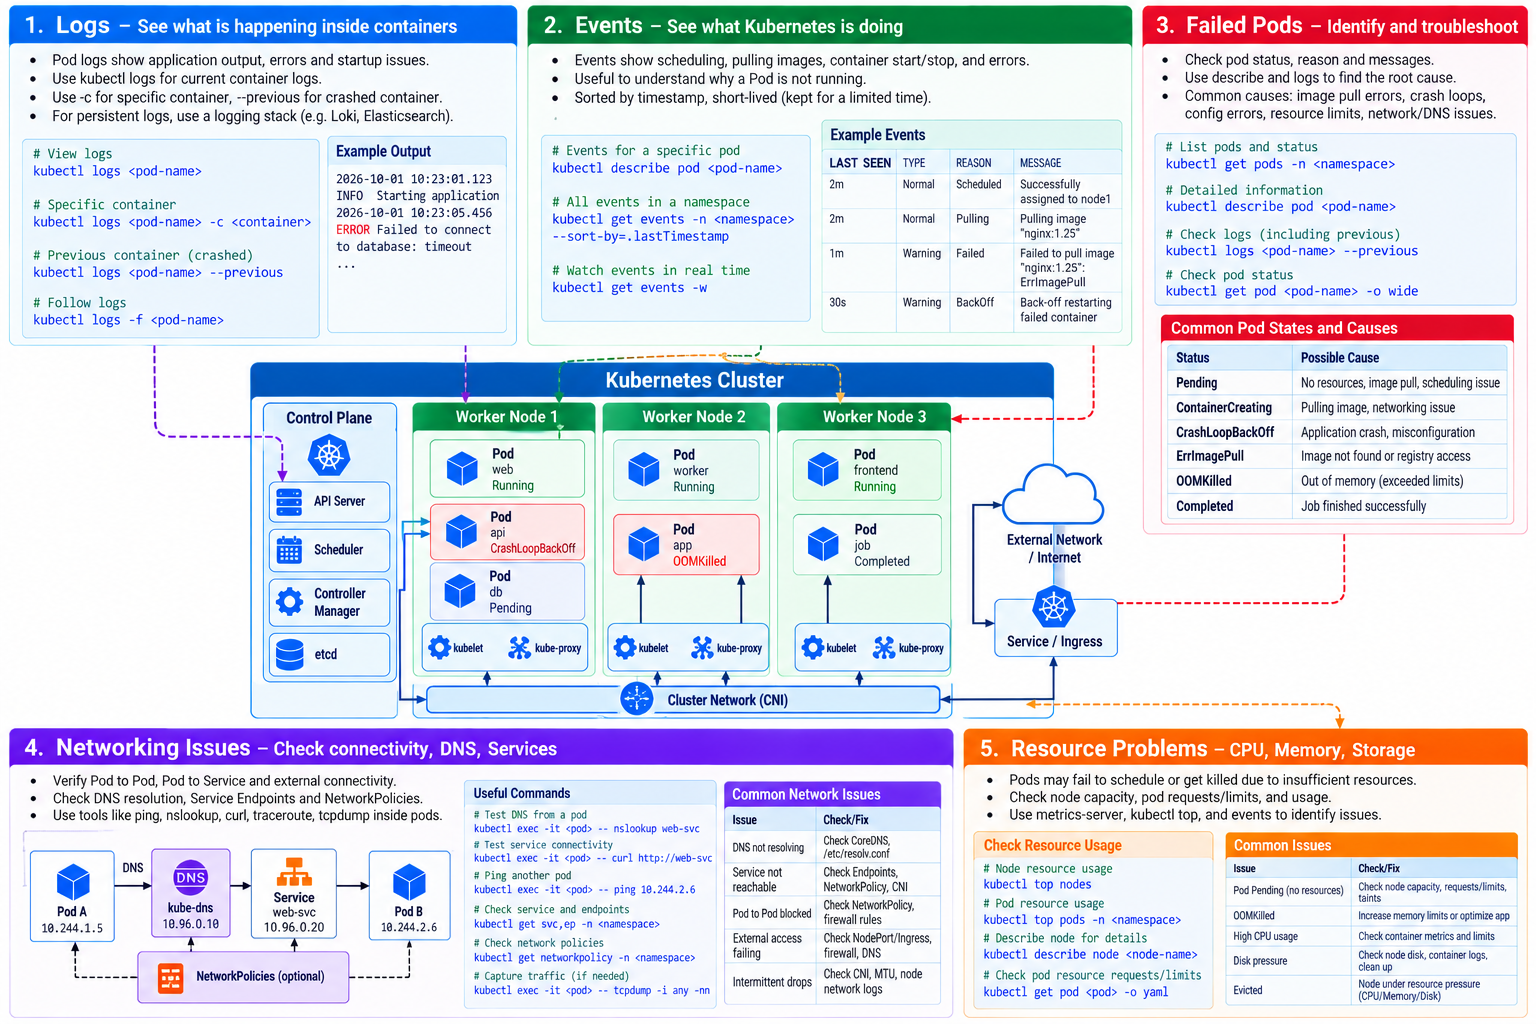
OOMKilled – Container killed due to out-of-memory condition.
ResourceQuota – Limits aggregate resource usage in a namespace.
LimitRange – Defines defaults and bounds for resource requests/limits.
PriorityClass – Defines a Pod’s scheduling priority.
- OBSERVABILITY AND TROUBLESHOOTING
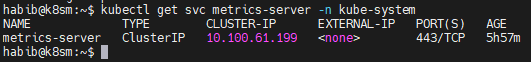
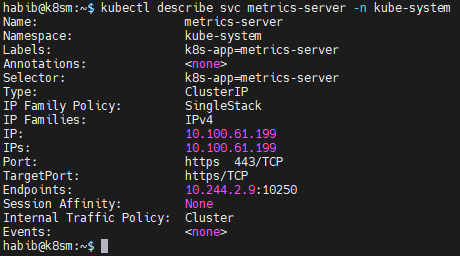
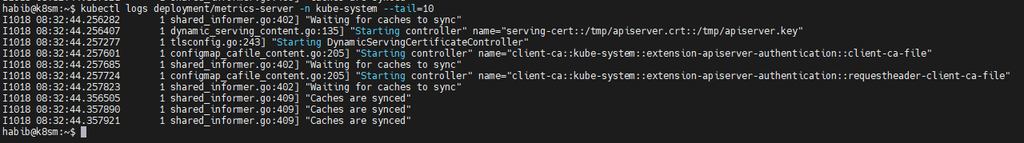
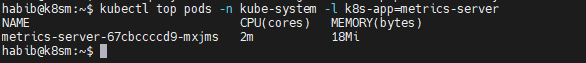
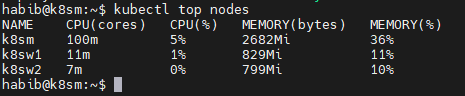
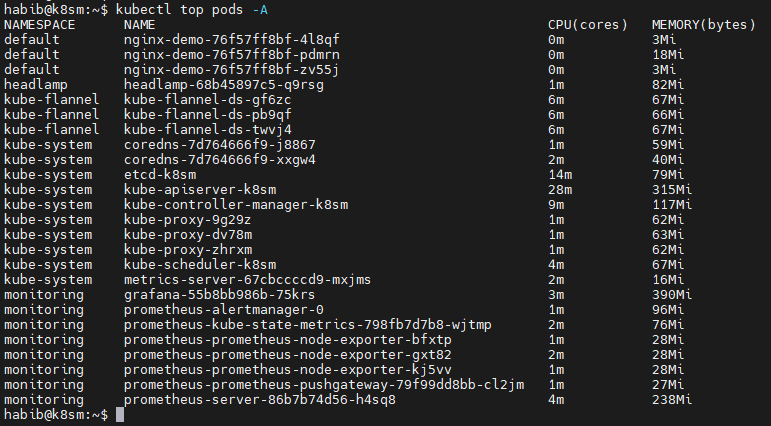
Metrics Server – Supplies resource metrics for kubectl top and HPA.
Prometheus – Metrics collection and time-series monitoring system.
Grafana – Dashboard and visualization platform.
kube-state-metrics (KSM) – Exposes Kubernetes object-state metrics.
Node Exporter – Exposes node OS and hardware metrics.
OpenTelemetry (OTel) – Framework for metrics, logs, and traces.
CRI-O – Kubernetes-compatible container runtime.
containerd – Container runtime commonly used with Kubernetes.
CrashLoopBackOff – Repeated container crashes with increasing restart delay.
ImagePullBackOff – Backoff after unsuccessful image pull attempts.
ErrImagePull – Image retrieval failed.
Pending Pod – accepted but not fully set up to run.
Running Pod – bound to a node; containers created, starting, or running.
Liveness – Probe Detects when a container should be restarted.
Readiness – Probe Controls whether a Pod is ready for Service traffic.
Startup Probe -Allows slow-starting applications to initialize.
Events Records – of notable resource-related occurrences.
kubectl logs – Displays container logs.
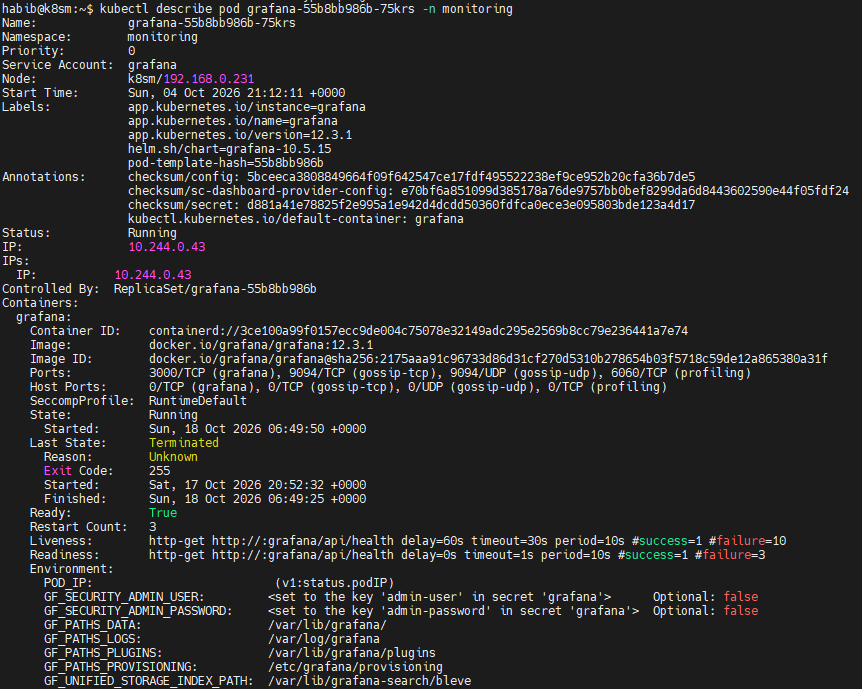
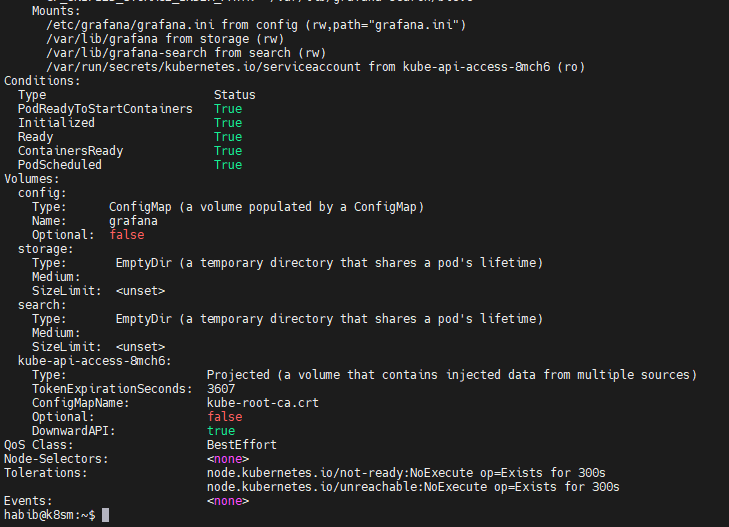
kubectl describe – Shows resource details and related events.
kubectl top – Displays resource usage when metrics are available.
- INSTALLATION AND LIFECYCLE
kubeadm – Tool for bootstrapping Kubernetes clusters.
kubeadm init – Initializes a control plane.
kubeadm join – Adds a node to an existing cluster.
kubeadm upgrade – Assists with upgrades of kubeadm-managed clusters.
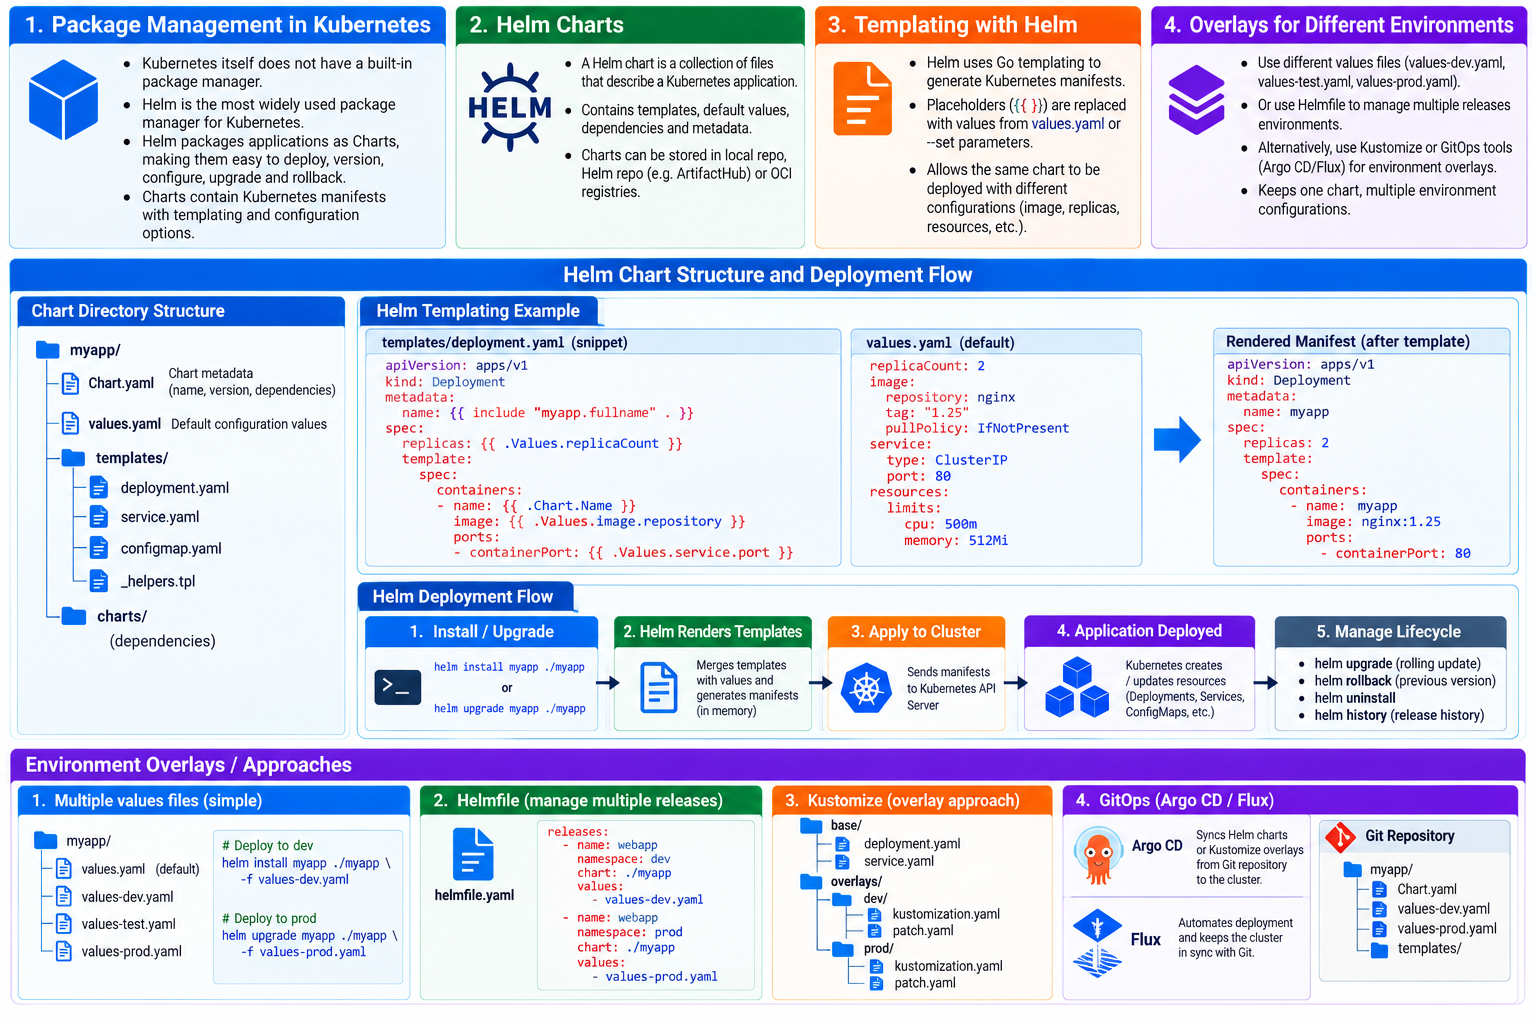
Helm – Kubernetes package manager.
Chart – Package of Kubernetes resources for Helm.
Release – Installed instance of a Helm chart.
Kustomize – Tool for customizing Kubernetes YAML configuration.
GitOps – Git-driven declarative deployment/operations approach.
Argo CD – GitOps continuous delivery controller.
Flux – GitOps toolkit for Kubernetes.
Drain – Evicts eligible Pods for node maintenance.
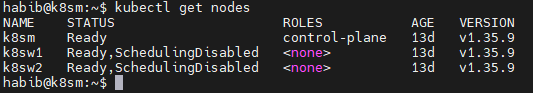
Cordon – Marks a node unschedulable.
Uncordon – Marks a node schedulable again.
- ADVANCED CLOUD-NATIVE TERMS
CR – Custom Resource; instance of a custom API type.
Operator – Controller using Kubernetes APIs to manage applications.
API Aggregation – Adds extension API servers to Kubernetes API surface.
Webhook – HTTP callback used for admission or integration.
Service Mesh – Infrastructure for service-to-service traffic management.
Istio – Service mesh platform.
Envoy – High-performance network proxy.
gRPC – Remote Procedure Call framework.
HTTP/2 – Hypertext Transfer Protocol version 2.
OPA – Open Policy Agent.
Kyverno – Kubernetes-native policy engine.
KEDA Kubernetes Event-driven Autoscaling.
Karpenter – Kubernetes node provisioning/lifecycle system.
Cluster Autoscaler – Adjusts node group sizes to meet workload needs.
SLO – Service Level Objective.
SLI – Service Level Indicator.
SLA – Service Level Agreement.
RTO – Recovery Time Objective.
RPO – Recovery Point Objective.
DR – Disaster Recovery.
- COMMON KUBECTL RESOURCE SHORT NAMES
Pods po – kubectl get po
Deployments – deploy kubectl get deploy
Services svc – kubectl get svc
Namespaces ns – kubectl get ns
Nodes no – kubectl get no
ReplicaSets rs – kubectl get rs
DaemonSets ds – kubectl get ds
StatefulSets sts – kubectl get sts
ConfigMaps cm – kubectl get cm
ServiceAccounts sa – kubectl get sa
PersistentVolumes pv – kubectl get pv
PersistentVolumeClaims pvc – kubectl get pvc
StorageClasses sc – kubectl get sc
NetworkPolicies netpol – kubectl get netpol
HorizontalPodAutoscalers hpa – kubectl get hpa
PodDisruptionBudgets pdb – kubectl get pdb
CronJobs cj – kubectl get cj
Ingresses ing – kubectl get ing
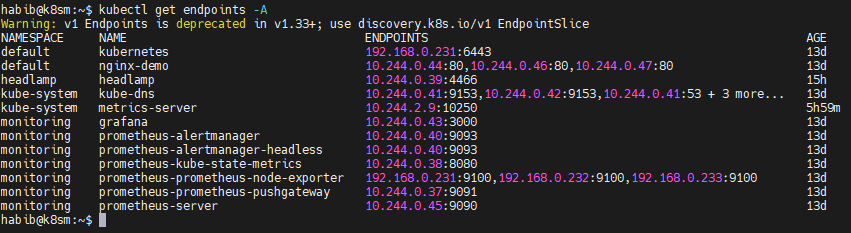
Endpoints ep – kubectl get ep
- TOP 20 CKA STUDY AREAS
- Pods and Deployments
- ReplicaSets
- StatefulSets and DaemonSets
- Jobs and CronJobs
- Services and DNS
- NetworkPolicies
- PersistentVolumes and PVCs
- StorageClasses
- RBAC and ServiceAccounts
- ConfigMaps and Secrets
- Taints and tolerations
- Node affinity and Pod affinity
- Resource requests and limits
- Liveness, readiness, and startup probes
- etcd backup and restore
- kubeadm installation and upgrades
- Node drain, cordon, and uncordon
- Pod and node troubleshooting
- Helm and Kustomize
- Cluster networking and CNI troubleshooting
RECOMMENDED LEARNING ORDER
Fundamentals -> Architecture -> Workloads -> Networking -> Storage ->
Security -> Scheduling -> Troubleshooting -> Cluster Administration
REFERENCES
Kubernetes documentation: https://kubernetes.io/docs/home/
CKA certification: https://www.cncf.io/training/certification/cka/
END OF DOCUMENT