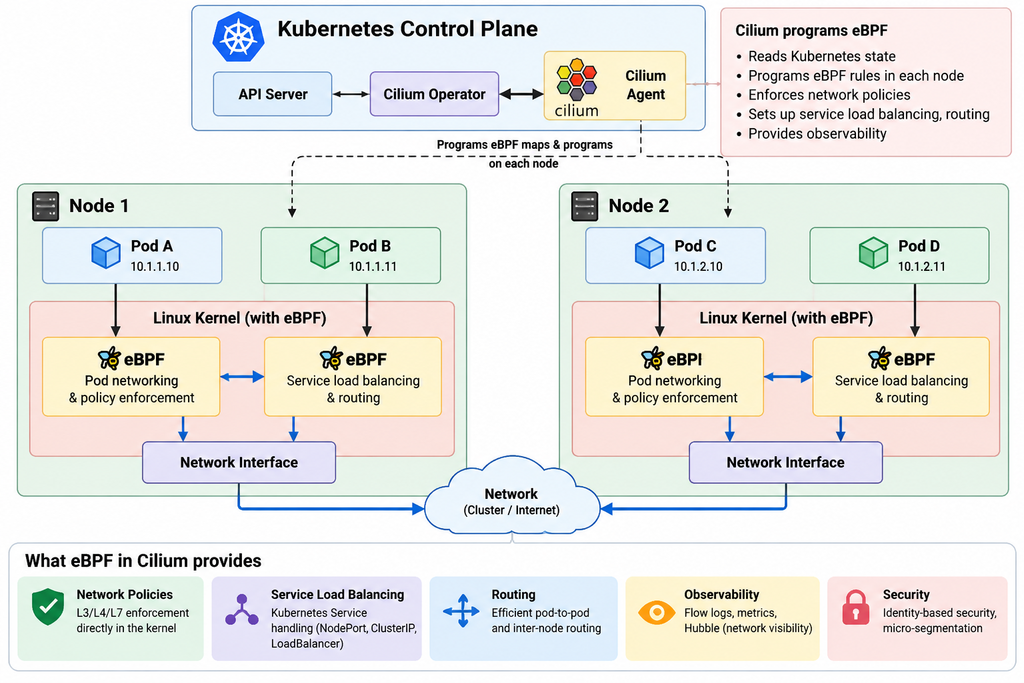
eBPF (extended Berkeley Packet Filter) is a Linux kernel technology that allows small, secure programs to run directly inside the kernel without modifying kernel source code.
In Cilium, eBPF is mainly used for:
- High-performance networking between Kubernetes pods and nodes
- Network policy & security enforcement
- Service load balancing and routing
- Traffic monitoring & observability with Hubble
- Reducing or replacing traditional iptables-based packet processing
In short: eBPF gives Cilium a programmable, efficient way to control and observe network traffic directly inside the Linux kernel.
In simple terms:
Pod → eBPF (Cilium) → Network → eBPF → Pod
eBPF allows Cilium to provide things such as network policies, load balancing, routing, service handling, and network visibility, often without relying heavily on traditional iptables.